Tag: Wordfence

  • WordPress Security Guide: Protect Your Site from Cyber Threats with George Lerner’s Expert Tips

    WordPress Security Guide: Protect Your Site from Cyber Threats with George Lerner’s Expert Tips

    Welcome to the companion webpage for my WordPress Security Presentation. This page provides comprehensive details on all the topics covered during the presentation.

    Hello, I’m George Lerner, your guide through the intricate world of WordPress. Whether you’re a course creator, a life coach, a passionate blogger, or an aspiring website owner, the digital landscape can often feel like a maze.

    My course, “WordPress Websites: From Overwhelm to Mastery”, is tailored to transform your experience of making and marketing your website or online course. I will cover the most confusing or frustrating or overwhelming parts of making and maintaining your website, so you know what to do and how to proceed, with confidence and mastery.

    In this introduction to my full course, I will explore actionable security advice for WordPress users, from beginners to advanced developers. Let’s dive in!

    Are you ever plagued by the fear of your WordPress website being vulnerable to cyber attacks and potential data breaches? Do you sometimes lie awake at night, worrying about the devastating consequences that a hacked website could have on your business or personal brand? 

    Imagine the peace of mind you’ll experience knowing that your website is impenetrable, your visitors are safe, and your hard work is secure. Get ready to say goodbye to sleepless nights and hello to a worry-free online presence.

    Most website attacks are against any website they can find — hackers probably probe your site hundreds of times a day. It’s time to take control and safeguard your WordPress website like never before.

    • Overview
      • This presentation is designed to provide straightforward, actionable steps and advice for enhancing the security of your WordPress website.
      • I will also cover security topics directly affecting your website, though outside of WordPress.
      • This is tailored to a wide range of people, from those just starting your WordPress journey to highly experienced website developers.
      • I will focus on security measures that you can implement directly on your WordPress site and those services you use associated with your website.
    • What Will Not Be Covered Here
      • I will not delve into areas that are solely controlled by your website hosting company, content delivery network, or other technical things you can’t control. If hackers get into those companies, there’s nothing you can do about it.
      • Nothing about the intricacies of security in plugin development. While this is a very important part of WordPress security, it is only for developers.
      • I also won’t cover attacks on you or your company specifically. There are many ways of finding out about a company, sometimes as simple as keeping an “open ear” at the local café. If a world-class hacker group or government intelligence agency wants your information, they are going to get it.

    Why Worry About Security?

    In today’s digital age, where cyber threats are becoming increasingly sophisticated, it’s crucial to protect your online presence from potential hackers and malicious attacks. 

    Even if your content doesn’t seem enticing to hackers, your hosting account is valuable. Therefore, securing your WordPress site should be a top priority.

    • The Importance of Prioritizing Security
      • Even if you believe that your content isn’t of interest to any hackers, it’s crucial to understand that your hosting account itself holds significant value. Many hacks are to control your site, not to get information.
      • Hackers can exploit your site to generate revenue by placing ads, or links that could potentially enhance the ranking of another site.
      • If they crack your password, it provides them with a blueprint to breach other websites more effectively. People tend to make passwords the same ways, or even use the same passwords.
      • They can use your account as a storage space for their customers to download files, thereby saving on their storage expenses.
      • Furthermore, the computing power of your account could be combined with thousands of other accounts, to launch a massive attack on a high-value website.

    Hackers Using Your Site Among Thousands

    Hackers can coordinate thousands of computers to guess passwords of millions of websites, making it hard for security software to track the attacks. To counter this, ensure you have software that checks for unauthorized changes on your site and alerts you to change your password promptly.

    • Understanding the Way Hackers Think
      • Hackers often orchestrate large-scale operations involving thousands of computers attempting to crack passwords of millions of websites. Each hosting account tries a random password from their list against a random website from their list.
        • Due to the sheer volume of IP addresses involved, even robust security software on thousands of websites might struggle to track which computer is attacking where on the network.
        • Moreover, these attempts may not even register as an attack, as they may appear as sporadic incorrect password attempts from unknown IP addresses, too infrequent to raise any alarms.
      • The solution to counter such “password cracking gangs” is not to limit your security measures to a few aspects of your website.
        • For instance, even if someone manages to obtain your password, you should have software in place that checks for unauthorized installation of new plugins or modifications to existing plugins or themes, or new admin users.
        • This way, even if they know your password, they can’t do much damage.
        • You would be alerted to change your password, and any unauthorized changes they made could be promptly deleted.

    Is There a Single, Foolproof Defense? No.

    A fundamental principle of website security is to deploy multiple strategies for detecting and thwarting attacks. Given that hackers continually refine their attack methodologies, it is imperative that you employ a variety of defenses to counter them.

    • Choose a reliable hosting provider with strong security measures
    • Create strong and unique passwords for all accounts
    • Regularly update plugins and themes to fix security vulnerabilities
    • Install a website application firewall for blocking password-guessing attacks, preventing malware, detecting bad people accessing your site.
    • Use secure connections (HTTPS) for your website, and for your Wi-Fi router
    • Separate your website delivery server from your website making server
    • and More

    Use Excellent Hosting – security, support, speed

    Choosing a hosting provider that focuses on security, is crucial. Select a hosting provider endorsed by those in your WordPress community who manage client sites.

    They see more problems on more sites, including sites with problems from the hosting company before the client moved to them; they have fixed more problems, so they know what to look for; they know about more plugins, more themes, and types of websites with more needs.

    The best hosting companies offer WordPress-specific excellent security, great support, and fast page load times.

    • Choosing the Right Hosting
      • Ignore social media comments, ads, and people who are not sure what their hosting company provides.
      • Ignore people who say they’ve been with a host for years with “no problems”. This means they likely have not been checking for problems, and likely don’t know if they have already been hacked.
      • Ignore hosting companies that don’t offer specific enhancements for WordPress sites. Security, technical support, page caching, database configuration, and more, must be fine-tuned to WordPress needs.
      • Outdated server software is an immediate disqualifier. Update your PHP version to the latest version available on the host. (As of February 2024, look for version 8.2 or 8.3) https://www.php.net/supported-versions.php says PHP7.__ does not get active support, nor updates “for critical security issues only”. Must be recent versions for database (usually MySQL or MariaDB), Linux, server (usually Apache or NGINX; don’t use IIS), server caches, etc. If they don’t know how to reliably update their software, they don’t know how to prevent errors on your site.
      • Opt for hosting within your budget that offers both superior security and exceptional customer support. Technical support quality is strongly tied to security quality; the company has to be skilled at both.
      • The best hosting companies also ensure rapid page load times, even for intricate eCommerce sites via slow mobile phones.
      • Here are some top-notch hosting services you might want to consider: 10Web (lc.lndo.site/10web), SiteDistrict.com, SiteGround, A2 Hosting. These hosting companies are reasonably priced, billed annually at about $120, and for most sites nothing else is needed.
      • There is one (and only one) free hosting to ever consider: wordpress.com offers free hosting that is reliable and secure.
    Your subscription could not be saved. Please try again.
    Your subscription has been successful.

    Newsletter

    Subscribe to my newsletter and learn when “WordPress Websites from Overwhelm to Mastery” is open.


    Your email address is only used to send you my newsletter and information about my course. 


    Unsubscribe anytime using the link included in every email.

    We use Brevo as our marketing platform. By clicking below to submit this form, you acknowledge that the information you provided will be transferred to Brevo for processing in accordance with their terms of use

    Content Delivery Network – speed and security

    A Content Delivery Network (CDN) like Cloudflare can deliver pages fast to your visitors while blocking “bad visitors” before they reach your hosting server. This not only reduces the resources your hosting account uses but also improves your site’s security.

    • The Role of a Content Delivery Network (CDN)
      • A CDN not only ensures swift page delivery to your legitimate visitors but also bolsters security.
      • Services like the free version of Cloudflare can effectively block a significant number of “bad visitors” before they even reach your hosting company’s server, reducing the resources consumed by your hosting account. You won’t get charged by your hosting company for hacker “excess traffic” or CPU or RAM use.
      • Hackers are exposed to cached pages of your site, not the WordPress program that generates your site. If the CDN determines any of your pages have changed, it requests updated copies of them from WordPress.
      • Consider upgrading to a paid version of Cloudflare, only after you have secured top-quality hosting and your site is making you money.
      • A CDN maintains a network list of malware signatures and current hacker IP addresses, enabling it to detect a hacker anywhere on the network and block them across the entire network.
      • However, it’s important to note that a CDN doesn’t replace all the comprehensive security measures provided by tools like Wordfence.

    Wordfence — Many More Ways of Preventing Hackers

    Wordfence offers additional security features that a CDN won’t, such as Two-Factor Authentication, blocking repeated password guessing attempts, Web Application Firewall, email alerts for plugin/theme updates, and scanning for modified plugins and themes.

    • Leveraging Wordfence for Enhanced Security Measures
      • Update Wordfence automatically when a new version is released?
        • Enable this, to stay up to date with the latest security features.
      • Two-Factor Authentication: That mildly annoying “type in a code” really works, to add an extra layer of security.
        • Use 2FA included with your anti-virus, or Google Authenticator.
      • Block Repeated Login Attempts: Prevent repeated attempts to guess passwords. Also, block common usernames hackers will guess, such as ‘admin’, ‘administrator’, or your domain name.
      • Web Application Firewall: This feature is still crucial even with a CDN, as it blocks additional types of malicious visitors. If a hacker figures out one way to bypass security, have another security rule still blocking it.
      • Email Alerts: Get notified when there’s an available update for a plugin/theme, especially if it includes a security patch.
      • Disable Code Execution for Uploads directory
        • This is vital for security, as it prevents hackers from executing any files in that directory.
        • Many plugins allow uploading files, always in the uploads folder. Hackers can try to upload malware.
      • Scan for Modified Plugins and Themes: This feature compares your plugins and themes against the WordPress Repository, alerting you to any unauthorized changes. It also alerts you to plugins that haven’t been updated in a long time or have been removed from the Repository, indicating potential security risks, and future server or WordPress updates could be make the plugin incompatible.
      • Report New Administrator Users: Get alerts when new administrator users are created, especially if you didn’t authorize it.
      • Report Files with Sensitive Information: Wordfence will notify you if files containing sensitive information (like wp-config.php or backups) are accessible from the Internet.
      • For a detailed guide on how to set every Wordfence setting, visit my website at lc.lndo.site/wordfence.
    Your subscription could not be saved. Please try again.
    Your subscription has been successful.

    Newsletter

    Subscribe to my newsletter and learn when “WordPress Websites from Overwhelm to Mastery” is open.


    Your email address is only used to send you my newsletter and information about my course. 


    Unsubscribe anytime using the link included in every email.

    We use Brevo as our marketing platform. By clicking below to submit this form, you acknowledge that the information you provided will be transferred to Brevo for processing in accordance with their terms of use

    Top Settings of Wordfence

    I have another page for every setting of Wordfence, and here are the most important ones.

    • Update Wordfence automatically when a new version is released?
      • Enable this, to stay up to date with the latest security features. Automatically updates Wordfence to the newest version within 24 hours of a new release.
    • Where to email alerts
      • Put your webmaster’s email address, or whoever should receive technical emails about security issues and plugin updates. You can add multiple email addresses here and separate them using commas.
    • Disable Code Execution for Uploads directory
      • This is vital for security as it prevents hackers from executing any files in that directory.
      • Many plugins allow uploading files, and always in the uploads folder. Hackers can try to upload malware.
    • Web Application Firewall Status
      • When you are first installing Wordfence, you will want “Learning Mode”. This gives Wordfence an opportunity to see what your plugins do normally. Also can use Learning Mode to test if a new plugin isn’t working because Wordfence is interfering — but always consider Wordfence might be right to block something, maybe it is the plugin that is bad. After a learning period, Wordfence switches to “Enabled and Protecting”.
    • Protection Level
      • You always want Extended Protection enabled
    • Enable brute force protection
      • Enable blocking “brute force” login password guessing attacks, trying millions of passwords.
      • Don’t have another plugin that does the same thing; disable that other plugin or that feature in the other plugin. Wordfence does this in the WAF.
    • Immediately lock out invalid usernames
      • The list of “invalid usernames” should include “admin”, “administrator”, “webmaster”. Hackers know these are the most common user names for when a WordPress website is first created. Another common username is your domain name.
      • If you use admin or another “top pick” by hackers, log in with an administrator account, make a new administrator account with a better user name (e.g. your name followed by several random characters) and make a nickname in the Users account to display on your pages & posts (never display your login name on your site, only display a nickname). Then, delete the old admin user, and WordPress will prompt you for a username to assign that user’s posts to. Then add the now-deleted username to Wordfence’s list of usernames to block.
    • Prevent the use of passwords leaked in data breaches
      • I set this to ‘For all users with “publish posts” capability’
    • Enforce strong passwords
      • Set to ‘Force admins and publishers to use strong passwords’
    • Prevent users registering ‘admin’ username if it doesn’t exist
      • This is Important, so you can immediately ban any IP address trying to login with the default WordPress user name.
      • Do not allow anyone else to make the user ‘admin’, as they could fool others to disclose sensitive information.
    • Participate in the Real-Time Wordfence Security Network
      • Let Wordfence on your site take advantage of knowledge from the entire Wordfence network, including hostile IP addresses and malware detection.
    • In Scan Options, the entire General Options section
      • Exception: these two entries
        • Scan files outside your WordPress installation
        • Scan images, binary, and other files as if they were executable
        • You don’t need these. If you like, you can occasionally run a scan with these set, and then un-check these again.
    • Wordfence Emails
      • Regularly scan through the emails Wordfence sends you. This will help you get familiar with what is normal and identify any abnormal activities or suspicious behavior.
      • Pay attention to the “Top 10 Failed Logins” section, as it may indicate a customer forgetting their password. Ignore the other failed logins, they are blocked hacking attempts.
      • Keep an eye on the “Recently Modified Files” list. Take note of any files that you don’t recognize or that seem out of place. While most of the files will be normal and harmless (mostly cached files or .css style sheets), watch out for any unknown files that could be a sign of hackers trying to gain access to your website. Wordfence is better than most security plugins, not often listing a plugin update as “modified”; it checks plugin files against the WordPress Repository.
      • I ignore “Top 10 IPs Blocked”, and “Top 10 Countries Blocked”; there is nothing to learn from those. “Recently Blocked Attacks” will likely be dozens to thousands every day; say “good, Wordfence is working”. If you are using excellent hosting and a CDN like Cloudflare, more attacks will be blocked before getting to Wordfence.

    Password Keeper — logins and other structured data, secure

    A Password Keeper will automatically create, securely store, and manage complex passwords for all your online accounts. It also provides a secure repository to safeguard several types of sensitive information, such as hosting account info, FTP connections, SSH keys, credit cards, software licenses, and notes.

    All information is encrypted with your “master password” before being transmitted across the Internet; as long as your master password is “lifetime secure”, hackers can’t get your unencrypted information.

    What a steal

    What’s happening: You might want to change your passwords ASAP.

    Here’s why: Last month, nearly 10 billion passwords were uploaded on a hacking site. It’s being called the largest password leak of all time.

    What it means for you:

    It’s much easier for someone to empty your bank account, run up your credit cards, or steal your identity if they can access sites where you’ve stored financial and other personal info.

    So consider updating your passwords—a strong one is 12 characters long with a mix of numbers, symbols, and lower and uppercase letters, says the Federal Trade Commission.

    Don’t reuse passwords from site to site, and avoid sharing them on calls or in emails or texts.

    Enabling 2-factor authentication, which requires an additional step beyond entering a password to access an account, might also help shore up your logins.

    from Fidelity Smart Money newsletter, August 20, 2024
    • The Importance of a Password Keeper for Secure and Convenient Password Management
      • Traditional methods of coming up with “strong” passwords can now be cracked within minutes to days. The top 1 million passwords, and top million username + password combinations, are readily available for hackers as “password cracker dictionary entries”.
      • Use a password keeper software to generate and remember long, random passwords.
      • Create a unique password for each website. You should not use your bank’s password on your local pizza restaurant’s website.
        • There are exceptions for alias domain names for the same site. For instance, Google owns YouTube and you log into YouTube with your Google account. Password keepers are aware of common aliases, and you can specify others if you need to.
        • It’s best to create a new password for your testing site when you copy your production site, though setting up an alias is acceptable.
      • Information to Store in Your Password Keeper:
        • Not just passwords, they have predefined fields for many types of information, and note fields for each.
        • Store your SFTP connection, SSH keys, hosting company info, domain registration info, email hosting, credit cards, Wi-Fi passwords, and more.
        • You can also store website client contact info (if you don’t have dedicated software for managing contacts), their social media details, everything you want to keep for making their webpages, social media accounts, videos, ads.
        • Store your Google ReCaptcha keys, software licenses, payment processor info, and any other information you want to access anywhere.
      • Choosing the Right Password Keeper Software:
        • Avoid using browser password storage, or iCloud or similar services to synchronize passwords on your browser. It’s too easy to have unsynchronized passwords on your different devices. They can’t store all the types of data that password keepers can.
        • The best antivirus programs for Windows or OS/X usually include password keepers.
          The Best Antivirus Software for 2023 | PCMag https://www.pcmag.com/picks/the-best-antivirus-protection
          The Best Free Antivirus Software for 2023 | PCMag https://www.pcmag.com/picks/the-best-free-antivirus-protection
          Most work with several operating systems (Windows, OS/X, Android, iOS).
        • LastPass.com is a free and cross-platform password keeper. Its paid version offers better sharing options and supports multiple devices.
        • Install the app on your phone and desktop, and add the browser extension in each of your web browsers.
      • Securing Your Password Keeper:
        • Make your Password Keeper’s Master Password “lifetime secure”, easy to type, and unforgettable. Visit lc.lndo.site/password for tips on creating such a password, such as picking a “movie mini-scene” and describing it in 5 to 7 words, preferrably including a word not in the “top 5,000 words of the English language”.
        • Keep your phone or computer locked when not in use and set your password keeper to lock after a brief period of inactivity.
      • Make hackers guess both your username and password simultaneously. Don’t use “admin” as a WordPress username; see above “Immediately lock out invalid usernames”.
      • Turn off your browser’s saving passwords. Don’t get confused by having passwords in two places. As you login to a site not yet in your password keeper, it will ask to save the new password; once the password isn’t needed in your browser’s password storage, you can delete it from the browser.

    Secure Connections to Your Website

    Always use secure connections like HTTPS, SFTP, and SSH to protect your WordPress logins and connect securely over insecure Wi-Fi. FileZilla and most other FTP programs offer SFTP, so you should always use secure FTP. Ensure your home and office Wi-Fi uses the latest security protocols.

    • Ensuring Secure Connections to Your Website (HTTPS, SFTP, SSH)
      • Always use HTTPS to protect your WordPress logins. Over HTTP, your WordPress username and password are transmitted from the login form to your site without any security.
      • Always connect securely, even over unsecured Wi-Fi, by using HTTPS, SFTP, and SSH.
      • Use FileZilla for SFTP and avoid plain FTP. If your hosting company doesn’t offer SFTP, it’s time to switch.
      • Implement the latest Wi-Fi security protocols on your home and office Wi-Fi networks.
        • Disable WPS (Wi-Fi Protected Setup) on your router. Exception: for a few minutes while you’re connecting someone.
        • For the best security, set your router to use WPA3 + AES-CCMP/AES-GCMP if it has it, or else WPA2 + AES. As you move down the list (WPA2 + AES, WPA + AES, WPA + TKIP/AES, WPA + TKIP, and worst WEP), you’re getting less security for your network.
      • Consider isolating your “Internet of Things” (IoT) devices (like security cameras, refrigerators, thermostats) from your computers.
        • IoT devices, like an Internet-enabled baby monitor, are powerful computers connected to the Internet, often without sufficient security measures, or even with known insecure software.
        • These devices can communicate with unknown servers and receive new tasks if they’re hacked. In large numbers, they can launch significant attacks.
        • Place these devices on a separate Wi-Fi router, connected to your main router, with guest permissions for internet access. They should have no access to your computers on the main router.
        • To stream videos from your phone to your TV, disconnect your phone from your main Wi-Fi and connect it to the IoT Wi-Fi.
        • For more information on how to use more capable routers to prevent IoT devices from attacking each other, and restricting internet access for your IoT device to a whitelist of allowed domains, visit Beyond Three Dumb Routers – pcWRT.
        • For more on securing IoT devices, see Steve Gibson’s Three Router Solution to IOT Insecurity – PC Perspective.

    Plugins and Themes

    I know, you were wondering when I’d mention this, right? Update plugins and themes frequently and only install ones recommended by your WordPress community experts. Avoid plugins from outside the WordPress Repository and minimize the number of plugins you use. For themes, opt for block-based ones like TwentyTwentyThree or TwentyTwentyFour, Spectra One, or Kadence.

    • Adopting Best Practices for Plugin Management
      • Regularly update your plugins and themes, at least twice a month.
      • While a bad plugin update can be fixed in minutes, fixing a hacked site typically requires the expertise of a professional, such as Wordfence or Sucuri. If Wordfence alerts you to a plugin update that includes security improvements, update promptly.
      • Consult with your WordPress Meetup or user group for expert recommendations on the best plugins for specific purposes. For instance, the Arizona WordPress Meetup https://arizonawp.org/ has an active Slack channel.
      • Only install plugins from the WordPress Repository, with the exception of paid versions of plugins in the repository. Avoid plugins from “plugin shopping malls” that lack quality checks, update frequency, and malware protection.
      • Do not install plugins based solely on social media posts or advertisements.
      • Minimize the number of plugins you install. Delete any you’re not using.
      • Be aware that any plugin can have security issues. Check Wordfence emails regularly and promptly update any plugins with identified security issues. If a plugin has a security issue that isn’t swiftly resolved, replace it.
      • Learn how to install a specific version of a plugin in case you need to undo a bad update. For example, the wp-cli command allows you to update or install a specific version of a plugin; or you can download a version and install it as a “new” plugin.

    Choosing Themes (only the Best)

    Use themes such as TwentyTwentyThree, TwentyTwentyFour, Spectra One, or Kadence.

    • The color palette and fonts are the easiest elements to customize in a theme. If you find a website with colors you like, instruct your “computer person” to add those colors to your theme’s palette (in theme settings, theme.json, or as a child theme).
    • Don’t select a theme for its pretty images. You’ll likely change all the images anyways.
    • With Full-Site Editing, you can create your own site header and footer, modeled after any site you like. This is part of the Block Editor. You can even design different header/footer for specific pages.
    • These are block-based themes that have been extensively checked for security, and coded for fast site speed, which is crucial for user experience and search engine ranking.
    • Only use a theme that pays attention to accessibility, including working for your site visitors who can not use a mouse or need high-contrast color combinations or screen readers.

    Test and Learn on a Separate Site

    Use a Testing Site, so making mistakes while learning, doesn’t affect your website. Try a new plugin, or a new layout, or a new color palette, without breaking anything.

    • Local Development: Professional developers in the AZ WordPress Meetup highly recommend Local for local development. Free, cross-platform.
    • Lando is another local development tool, ideal for bug testing. It offers even more options than Local does, for different versions of Linux, database, WordPress, and PHP. Free, cross-platform.
    • Enable full debugging options on your testing site. Make sure these are logged to a file and not displayed on the screen.
    • Most top-tier website hosting companies offer an easy way to create a clone of your current website, known as a “staging” site.

    Email Security and Delivery

    • Managing Emails Effectively
      • Be cautious of phishing attempts and suspicious emails. Use email reader programs that alert you to the sender not being validated (Google Workspace and Zoho are among these). Don’t trust email links; for example, your bank will have important notices if you log into their site directly instead of using an email link. If your software says the message is spam or phishing, it usually is; if it says something more serious you should avoid every link.
      • Ensure that your emails originate from your domain name, not your email service’s domain name or your Internet provider. “Email Sender Reputation” matters!
      • Utilize services like Brevo, Google Workspace, or Zoho to send emails. This applies to all your newsletters, password reset requests, order confirmation emails, and other transactional emails.
        • These services enhance the delivery rate of your emails.
        • Your recipients are more likely to respond to your emails if their email software verifies your identity.
      • Set up your DNS records to include MX, DMARC, SPF, and DKIM. With these, your customer’s email software can verify your emails came from your domain, not a spammer. Spammers can easily pretend their email came from your account, putting anything in the “To:” and “From:” fields of emails. These DNS records are where you connect your email sending service to your domain’s email.
      • Consult your Domain Registrar and Email Hosting company for assistance in setting this up.
      • Never purchase email lists, that is unnecessary and damages your email reputation. Always require people opt-in to your email list. The best way to avoid being “blacklisted” is to “send high-quality content, relevant to people who opted-in to get it”.

    Further Resources

    • Further Resources for Enhanced Security
      • Reach out to your WordPress Meetup or user group, or the AZ WordPress Meetup’s Slack channel, for security advice and recommendations. Arizona WordPress Meetup top right corner link to the Slack channel.
      • Utilize the Wordfence support forums and subscribe to their newsletters for regular updates and insights.
      • Report any security bugs through the Wordfence secure bug reporting channel.
      • Explore the Wordfence YouTube channel for a wealth of information and tutorials on securing your WordPress site. Visit Wordfence YouTube for more.
  • Optimizing Wordfence Settings for Enhanced WordPress Security: A Configuration Guide

    Introduction to Wordfence

    As a WordPress website owner, one of your top priorities is ensuring the security of your site. This is where Wordfence comes in.

    Wordfence is a comprehensive security plugin for WordPress that provides a range of features designed to protect your website from hacks and malware. It offers a Web Application Firewall (WAF) that identifies and blocks malicious traffic, a malware scanner that checks core files, themes, and plugins for malware, bad URLs, backdoors, SEO spam, malicious redirects, and code injections, and a suite of additional features like live traffic monitoring and login security.

    Wordfence is designed to be user-friendly, even for those who aren’t tech-savvy. It’s easy to install and set up, and once it’s running, it works in the background to keep your site secure, giving you peace of mind and letting you focus on what you do best – creating great content and engaging with your audience.

    Now, let’s dive into how to access and navigate through the Wordfence settings to ensure optimal security for your WordPress site.

    Accessing Wordfence Settings

    To access the Wordfence settings page, follow these steps:

    1. In your WordPress dashboard, locate the main menu on the left-hand side.
    2. Click on “Wordfence”. This will open a sub-menu.
    3. In the sub-menu that appears, click on “All Options”.

    And there you have it! You’re now on the Wordfence settings page, where you can configure Wordfence to best protect your site.

    Wordfence License

    No configuration needed.

    View Customization

    • Check the box for “All Options” menu item for easy access.
    • Disable “Blocking” or “Live Traffic” menu items as they are not frequently used.

    General Wordfence Options

    • Update Wordfence automatically: Enable this for automatic updates.
      Note: If you’re using a LiteSpeed server, you will get a message to ensure the “noabort” environmental variable is set. Ask your website hosting company how you should (or better still, how they should) configure this.
    • Where to email alerts: Enter the email address of your webmaster or whoever should receive technical emails about security issues and plugin updates. You can add multiple email addresses separated by commas.
    • How does Wordfence get IPs: Use the recommended setting. If there’s a discrepancy between the “Detected IP(s)” and “Your IP with this setting”, contact your hosting company or technical person.
    • Look up visitor IP locations via Wordfence servers: Keep this enabled.
    • Hide WordPress version: Keep this enabled to make it harder for hackers to know your WordPress version.
    • Disable Code Execution for Uploads directory: This is crucial for security. It prevents anything in your uploads directory from being executed, protecting against potential malware uploads.
    • Pause live updates when window loses focus: Enable this to conserve server resources.
    • Update interval in seconds: A setting of 2 is good, but longer might be better.
    • Bypass the LiteSpeed “noabort” check: This is only needed if your server uses the LiteSpeed cache. Check with your hosting company about the LiteSpeed settings.
    • Delete Wordfence tables and data on deactivation: Leave this unchecked unless you’re deleting the Wordfence plugin and want to delete the data. (No, you don’t want to delete the Wordfence plugin!)

    Dashboard Notification Options

    • Updates Needed (Plugin, Theme, or Core): Enable this to stay informed.
    • Scan Status: Enable this to stay informed.

    Email Alert Preferences

    • Email me when Wordfence is automatically updated: Uncheck this unless you want to be notified.
    • Email me if Wordfence is deactivated: Check this. WordFence should never be deactivated without your knowledge.
    • Email me if the Wordfence Web Application Firewall is turned off: Check this. The firewall should always be active.
    • Alert me with scan results of this severity level or greater: Set this to Medium to avoid an overload of low-level alerts.
    • Alert when an IP address is blocked: Don’t enable this as your website likely blocks several IP addresses every hour.
    • Alert when someone is locked out from login: Enable this. It could be a customer who forgot their password or a hacker.
    • Alert when someone is blocked from logging in for using a password found in a breach: Enable this. It could be a customer who needs to be informed about the importance of using unique passwords.
    • Alert when the “lost password” form is used for a valid user: Enable this. It’s a common hacker trick to request a password reset.
    • Alert me when someone with administrator access signs in: Disable this if you regularly check for unauthorized administrator access.
    • Only alert me when that administrator signs in from a new device: Enable this. A new device in a different part of the world could indicate a stolen password.
    • Alert me when a non-admin user signs in: Disable this. You want people to be able to sign in.
    • Only alert me when that user signs in from a new device: Disable this unless you know your users well enough to tell if this is from a different part of the world.
    • Maximum email alerts to send per hour: Set this to 2. You don’t want to be overwhelmed with emails.

    Activity Report

    • Enable email summary: Set this to “Once a week” and review it every time. Get to know what a “normal” one looks like so you can spot anything unusual.
    • List of directories to exclude from recently modified file list: Exclude directories that you know are okay, such as those used by a plugin for its CSS files.
    • Enable activity report widget on the WordPress dashboard: Enable this on most sites, but disable it on sites where you want to minimize plugin resources.

    Basic Firewall Options

    These sometimes require account-level changes. Work with your technical support person and hosting company.

    • Web Application Firewall Status: When first installing Wordfence, set this to “Learning Mode”. After a learning period, Wordfence switches to “Enabled and Protecting”. Set this to the default that Wordfence suggests, most likely 7 days from now.
    • Protection Level: Enable Extended Protection.
    • Real-Time IP Blocklist: This is a premium feature. Free accounts have an IP Blocklist from the Wordfence network that is not updated as frequently.

    Advanced Firewall Options

    • Delay IP and Country blocking until after WordPress and plugins have loaded (only process firewall rules early): Leave this un-set.
    • Allowlisted IP addresses that bypass all rules: You shouldn’t need to bypass all rules for any IP addresses. If necessary, you can bypass a specific rule.
    • Allowlisted services: Enable for Sucuri and Facebook. Also enable for Uptime Robot, StatusCake, and ManageWP if you use these services. Enable for Seznam Search Engine if desired.
    • Immediately block IPs that access these URLs: You likely won’t need to specify any URLs here. Let Wordfence block via its normal methods. Keep these IP lists short, if not empty.
    • Ignored IP addresses for Wordfence Web Application Firewall alerting: This could be your IP address, but only while you are testing something on your site.
    • Rules: Leave all rules turned on unless advised otherwise by a Wordfence support person.
    • MANUALLY REFRESH RULES: This lets you get the latest rule set, even if you have the free version of Wordfence. Do this before running a manual scan.

    Brute Force Protection

    • Enable brute force protection: Always enable this.
    • Lock out after how many login failures: Lower this to 10. If you can’t get your password right in 10 tries, you’re doing it wrong.
    • Lock out after how many forgot password attempts: Set this at 5. This is how many times your “Forgot password?” form can be used.
    • Count failures over what time period: Set this to 4 hours. Some hackers try to fool website security by spreading out their attempts, so increasing this to 1 day is fine too.
    • Amount of time a user is locked out: Set this to 12 hours. Some hackers will try passwords rapidly, so this really thwarts them.
    • Immediately lock out invalid usernames: Enable this. The list of “invalid usernames” should include “admin”, “administrator”, “webmaster”.
    • Prevent the use of passwords leaked in data breaches: Set this to ‘For all users with “publish posts” capability’.
    • Enforce strong passwords: Set to ‘Force admins and publishers to use strong passwords’.
    • Don’t let WordPress reveal valid users in login errors: Enable this to make guessing your login much harder.
    • Prevent users registering ‘admin’ username if it doesn’t exist: Enable this to avoid confusion and potential security issues.
    • Prevent discovery of usernames through ‘/?author=N’ scans, the oEmbed API, the WordPress REST API, and WordPress XML Sitemaps: Enable this to make password crackers have to guess your login name.
    • Disable WordPress application passwords: Enable this. Application passwords allow a third-party site or application to access your site as your own login, but with a separate password.
    • Block IPs who send POST requests with blank User-Agent and Referer: Enable this. All web browsers and services are supposed to say “who they are” and what URL they are referred by.
    • Custom text shown on block pages: Leave this blank unless you want to give some message when a visitor gets blocked.
    • Check password strength on profile update: Enable this. This notifies you if someone is using a weak password. You can then train them to use strong passwords.
    • Participate in the Real-Time Wordfence Security Network: Enable this. This lets Wordfence on your site take advantage of knowledge from the entire network, especially bad IP addresses and malware detection.
  • Removing Hacks from Your Site

    Hi, I’ve been getting the same bunch of exe files uploaded to the root of my server for the past few weeks. I installed WordFence and also bought an expensive “Sitelock” service / firewall for $50 a month! Sadly my site is not making any money yet so this is a huge expense. I’m at my wits end and hope you can help. Thank you!

    Hopefully this isn’t about your site…

    There are many indications your site has been hacked. Seeing many unknown files is a clear sign. Seeing a warning from your web browser or Google Analytics is definitely something to take seriously. Seeing pages of your site listed in search engines containing content you didn’t write, is another common way of finding out your site is hacked.

    I would say you do not need both WordFence and Sitelock, especially since your site is not making money yet. Use WordFence, and many sites can use the free version unless you see a paid feature you really want.

    It is important to go through all the WordFence settings, to make sure that you have the most secure settings that will work on your hosting account. (Change a few settings, make sure everything works on your hosting account, then make more setting changes.)

    The WordFence application firewall is especially useful for blocking malware from spreading. For example, an image slider plugin that has a security vulnerability might allow a hacker to upload malware instead of an image; but the firewall would likely stop it from running, so there would be no damage to your website. (It would likely alert you to any attempts to run that file, and recommend you delete it.)

    Is the Site Still Hacked?

    How confident are you that you have found the source of the “bunch of exe files” and removed it? Almost nobody should attempt cleaning a hacked site themselves. It truly requires an expert. Hire WordFence to clean your site, using the money you have been paying to SiteLock. (I have nothing against SiteLock, but most sites will be adequately protected with WordFence, especially if you are using a good hosting company.)

    There are sites that offer “site scans”. However, these are not thorough assessments of every part of your hosting account. WordFence and Sucuri offer them, and they say clearly their free scans are not thorough.

    For example, some hackers install scripts that “stay asleep” for a while, to avoid detection, and only act when the hacker has work for them to do. Said another way, your site could have been hacked months before you noticed anything wrong, or a site check noticed anything.

    When the WordFence Application Firewall is installed on your site (different than scanning from outside your site), it can check every file for problems and every action your site takes, and every incoming request to your site. If the firewall reports your site is clean, you have much more certainty it is accurate.

    How to Prevent Many Hacking Attempts

    You should also look at removing plugins you do not need, and look at removing plugins that do not have excellent reviews in the WordPress plugin repository. Replace any plugins that have not had any updates recently. (Same rules apply for themes.) Do not simply deactivate them, you should delete them from all your WordPress installations. (Never have WordPress installations “lying around”, you must keep every installation of all your software updated.)

    The hacker could have gotten in through insecure plugins. Don’t install plugins that haven’t been thoroughly vetted by the WordPress repository, and by your most technical friends/colleagues (or better still, your WordPress Meetup). Keep all plugins updated, and WordPress updated — many of those updates include security patches.

    The hacker could have logged in as You, and installed malware. It is much easier than you think, for hackers to guess your password, unless you have a computer-generated password. Use a password keeper such as LastPass, have it store and fill in your login information on all sites you visit (and use it to store all other important data, e.g. your WiFi password, router administration login, credit card information, software licencse, etc.) Have your password keeper generate the longest password each site will accept (up to maybe 50 characters). No using the same password on different sites. See my Strong Passwords for WordPress for why you really need to use a password keeper, and how to make a hard-to-guess but easy-to-remember and easy-to-type password for your password keeper’s master password. (I also use a very good password for access to my computer.)

    Another way hackers could get your login information is by your not using SSL. You must have SSL on every website. Why do you need SSL? Because without it, anyone with WiFi sniffing software can see the plain-text information sent by your WordPress forms, including your login form. When SSL certificates were expensive and hard to install, the rule was you needed SSL if you were doing anything ecommerce; now SSL certificates are available (on all the good hosting companies) for free and installation is “click a button”.

    The hacker could have gotten in through your hosting company not having adequate security; now is a good time to assess whether you can evaluate hosting companies for WordPress security (most people can not). Many popular hosting companies have inadequate security.

    What Hosting Company to Use?

    The Arizona WordPress Meetup has many people who set up and maintain sites for clients, and they have identified very few hosting companies that are worth using for your website. I use SiteGround.

    SiteGround is probably about the same cost as your current hosting company, if you picked your hosting company by price (most people do). But SiteGround provides excellent technical support and excellent website security.

    On SiteGround and other excellent hosting companies, SSL certificates are free; unlike GoDaddy which charges more for SSL for a year than for hosting.

    As a website developer, SiteGround provides many tools to make my job easier.

    Could You Do It Yourself?

    If you can’t hire WordFence to clean your site, if your site is a small enough number of pages, make a copy of Just the Text and Just the Images of your site, of every page. Then have your hosting company Wipe your entire site completely clean, every file, the entire database, every configuration setting.

    Then install WordPress fresh, then WordFence right away, then only the plugins you need, then the default WordPress TwentyTwenty theme (or Astra theme) and Elementor page builder, and then remake all your posts.

    That is the only way to have any certainty the hack is removed, if you’re going to “do it yourself”.

  • WordPress Security for People Without Technical WordPress Knowledge

    WordPress Security for People Without Technical WordPress Knowledge

    What I’ll Cover

    • What your hosting company should do for security
    • Making secure passwords for any web site (and why what you’ve been doing probably isn’t good enough)
    • Password Keepers
    • Limiting Login Attempts, and Keeping your User Name hidden
    • Why you should Always do Automatic Updates and what you risk if you don’t
    • Block hacker files from executing, in the most common folders
    • WordPress Security Plugins you Must use

    Hosting Company Should Provide Security (but most Do Not)

    There is a lot that your host should do, to make your hosting account and your WordPress sites secure. (And by far, most hosting companies are negligent.) You should ask the technical support people lots of tough questions about security, and talk to your technical friends, and other WordPress users, about security.

    If your host isn’t giving good answers to security questions, and doesn’t improve Fast, then move to another host as soon as you can. (Though there are things that you have to do, there are far more that only your host should do.) Security is too important and too technical for most people to be able to do properly themselves, and it isn’t your job, it is your hosts’ job.

    The best hosting companies have top-quality security hardware, and special software, to block hackers, and have someone putting about 20 hours a week into researching the global security discussion boards for the latest threats, and putting security rules in place to block them. You can’t do that yourself, unless you can put those 20-30 hours per week into learning and implementing it.

    Ask the best anti-hacker security companies, and at your local WordPress Meetup or WordCamp, for hosts they are satisfied with for excellent technical support and excellent security. There are a few web hosting companies I recommend.

    There are, however, many things that affect security that only you can do, and things that you can do if your host isn’t doing their job.

    Use Password Keepers and Very Strong Passwords

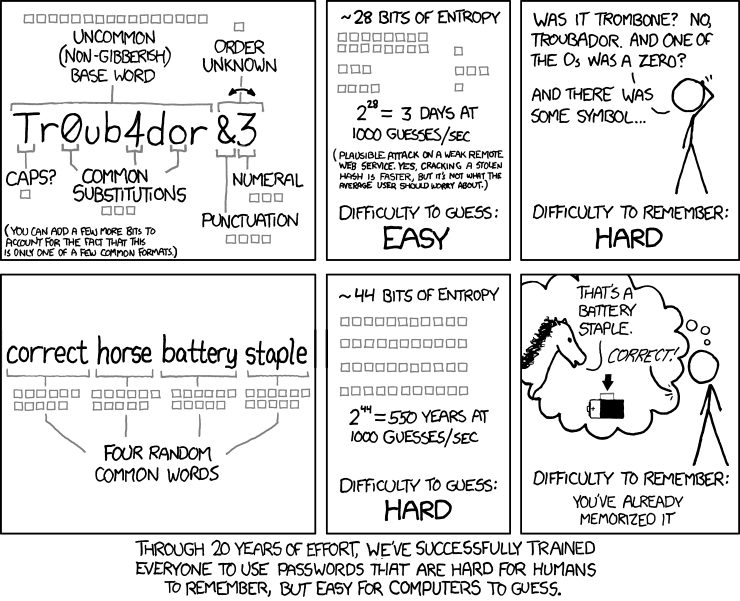
    The first of those is picking good passwords. Strong Passwords for WordPress and your Password Manager. This is essential. The ways we’ve been taught for decades, how to make passwords, as known to hackers, and using those rules makes passwords that are far to easy for hackers to guess.

    The “substitute a 3 for the first e” type of rule makes passwords that are hard for you to remember and hard to type, but easy for computers to guess. I teach you how to make passwords that are easy to remember, easy to type, and very hard for computers to guess (for your password keeper software and the few passwords you type often), and how to use computer-generated passwords stored in your password keeper for all other passwords.

    Using strong passwords is essential for Every site you log into. And each site should have a unique password, to reduce damage if a site’s data is stolen.

    Limit Login Attempts

    Given enough computers and time, hackers can guess any passwords that are not long strings of computer-generated random characters. So you should limit how many attempts they can make.

    There are WordPress plugins that limit the number of attempts at logging in, usually by IP address, within a short amount of time. These plugins also limit attempts at guessing passwords for the same user name. Violations result in being completely locked out of WordPress for a long time (60 minute lock-out for 5 attempts might be a good setting).

    Instead of being able to try the WordPress login form perhaps 100 to 1000 times every second, limit login attempts to 4 times every 5 minutes, and lock them out for an hour. (Hey, if you’re a lousy typist, with your long secure password, slow way down your third try and get it right!)

    I have seen over 100,000 attempts in a single night, on a small site where I deliberately left this open for a week. (With a WordPress Administrator user name that is not obvious, and a very strong password, you can test this. But block bad guys every way you can.)

    Suggested plugin: iThemes Security and/or WordFence are my overall favorite plugins for security. Some options you have to test if it works on your hosting account, or if it blocks something you need; and one of the options that will work on every WordPress site is the limit login attempts.

    WordFence is a direct competitor with iThemes Security and also excellent (if I were starting newly, I’d probably pick WordFence, it’s the most popular among technical people at WordPress Meetups).  I haven’t used it yet (simply because I know iThemes Security so well).

    Sucuri WP Plugin also has limiting logins as an option, excellent. (Works well with either iThemes Security or WordFence.) Among other features, has single-click run Sucuri Site Check on the current site.

    (Only use one plugin to limit logins, these plugins have this feature as an option.)

    Do Not Use (hasn’t been updated in over 4 years): Limit Login Attempts plugin, only compatible up to WordPress version 3.3.2. Even though it “seems to run” it still doesn’t check as many things as the plugins I mentioned. Any software that old is likely to stop working as WordPress changes.

    Periodically check for plugins that haven’t been updated in a long time. If they are actively being supported (check the support page for the plugin) and “keep working fine” that’s okay; but most often if a plugin isn’t being updated, the plugin author isn’t paying attention any more, and hackers can find holes that aren’t being filled.

    If you have a smart phone or tablet, definitely look into “2-Factor Authentication”, where you type a password and a short 2nd password delivered to your other device. Clef Two-Factor Authentication and Google Authenticator are excellent.

    Keep Your Administrator Login Name Secure

    Password Crackers expect your login name to be the WordPress default, “admin”. Some will look at pages and posts on your site, find who the author is, and try that for the login name. They also know that many “one button install” programs will take your hosting account name or domain name and put that in as your WordPress login. Don’t Do It!

    You should have one login for everyday editing pages (with Editor privileges), and a different login for administrative tasks such as updating and installing themes (with Administrator or Network Administrator privileges). I have the Profile, Admin Color Scheme set to Sunrise for the administrator user, so I can tell at a glance and remember to log out.

    It is easy for anyone to find the name for each users, for example https://molten-salt-reactor.lc.lndo.site/?author=1 shows the posts for the 1st author (?author=2, =3, etc.) The “display name” is shown on the top of the page. So, in the Profile screen, specify a Nickname, and for “Display name publicly as…”, select the nickname. Now the Author page, and themes that display the author of a page or post, aren’t giving away your login name.

    To change the administrator login name, use iThemes Security, which has a single-button way to do this; or you can log in as administrator, and create another user with administrator permissions. Then log in with that new user, and delete the user with the default login name.

    Block Logins at the Server Level

    Loading WordPress 100,000 extra times in a night is work for your server, taking up page loads and bandwidth that your hosting account might charge extra for.

    That many page loads at maximum speed slows your entire site down, for your actual visitors.

    You can put a server password on the WordPress login page. Minimal work for the server, easy to implement. Ask your technical person to put it in your .htaccess file. This doesn’t need to be a secure password, as these are bots not people trying 100,000 times; a simple riddle will work. Prompt “say hello there” with user name hello and password there. This adds security simply through being an extra step that is used on few sites.

    This double login is an extra step for you, but blocks a lot of nonsense. However, you wouldn’t want this for a membership site, where every member has to log in (unless of course you are teaching your members about security, right?)

    Automatic Updates

    I advise always doing WordPress theme and plugin updates quickly, at least every week. Then, after the theme and plugin updates, do any WordPress core updates.

    There are sometimes problems with a WordPress or a plugin update. Extremely rarely, that could take your site down. Less rarely, an important feature of a plugin would not work, especially if the plugin was written with out-dated programming practices.

    If there are important security fixes, WordPress will release the fix as soon as it is ready and passes their testing, but before all plugin authors have had several days to make sure their plugin works with the “pre-release” version of the security update.

    If you have someone on staff whose job includes doing all updates promptly after they are released but after testing on your important site (every day, no vacations, someone does this), you can keep doing WordPress and plugin and theme updates that way.

    For everyone else, keep automatic updates on. Even if there is a problem with a plugin, getting the update for the plugin in a few days (or replacing the plugin) is much less work than removing a hack from your site; much less damage to your reputation; much less inconvenience for your customers.

    Security first, then “backwards compatibility”.

    To minimize the chance of problems, I recommend updating your plugins and themes, and then update WordPress. Many of those plugin and theme updates will be to correct any problems with the new version of WordPress.

    Hackers love sites where updates were “forgotten about”, and still haven’t been done months or years after they were released. That means you have to update all of those “temporary” or “test” installations you have in your hosting account, too…

    Prevent Execution of PHP in WP-Content/Uploads

    Many hackers target plugins that have an “upload file” feature. (For example, upload images for a slider; or upload settings from the same plugin on another site, to make this site have the same settings.) Very useful in the plugin, but many plugin authors can’t check their work for security holes nearly as well as the hackers can. Once uploaded as a PHP file, or renamed to be one, the hackers know what location the plugin puts uploaded files in, and can execute it directly by the URL (bypassing loading WordPress, and any security in WordPress).

    This requires edits to your main .htaccess file and/or a .htaccess file in the wp-content/uploads folder. Most security plugins that have this feature will tell you what to paste in, if your .htaccess file is write protected (a very good idea). Keep your .htaccess files with permission 444, except 644 for the few minutes you are making a change.

    Sucuri WP Plugin has many WordPress “hardening” features, including blocking execution of files in vulnerable folders.

    Block Access to Critical Files

    Your .htaccess file, wp-config.php, and your site backups are files that should never be able to be accessed from the browser.

    Sucuri plugin (among others) blocks .htaccess and wp-config.php.

    Your backup software should create a .htaccess file in the backups folder (if you save it on the server, for example to FTP it to your computer; many backup programs will save the backup on other sites, e.g. DropBox or Amazon S3).

    FTP and XMLRPC Security

    Disable “anonymous FTP”. There was a use for it in 1980, not today. But many hosts have it enabled. Turn It Off.

    FTP doesn’t have a “limit logins” feature. Use the longest random password your host allows. If the host only allows 8 characters, throw a “lousy security tantrum”.

    XMLRPC attacks are fairly new. You can log in and post via XMLRPC. It reports back if your login was successful. Until 2014, this article says, none of the login limit plugins were checking this. Make sure yours does, if you truly need XMLRPC (I don’t). Of course, also make sure you have your password for XMLRPC is very strong (it is probably the same as your administrator password, but you can assign which users can use XMLRPC).

    WordPress Security Plugins

    iThemes Security is excellent.

    WordFence also excellent. You must install and configure either iThemes Security or WordFence or both.

    Block Bad Queries Pro (or free version, which has the same security rules but less nice user interface). If you don’t have the technical skill to edit .htaccess to paste in the suggested text, and don’t have a friend who does, this plugin is absolutely simple. It takes the hacker-phrases most often used, and blocks them. If you have .htaccess skills, or if you want to understand what Block Bad Queries does, read Building the 5G Blacklist and the 6G Blacklist is coming out soon.

    No conflicts with iThemes Security or Sucuri (5G Blacklist and iThemes and Sucuri do their security before WordPress loads, and if you have several of these loaded, the first one with a block for a specific “baddie” stops it completely).

    Get clean with Sucuri — this company is the expert at removing malware from WordPress sites, and has a firewall to block getting malware. They also have a free Sucuri Security Plugin – Auditing, Malware Scanner and Security Hardening. Also, frequently run their free quick scan of your site.

    What’s Next?

    Please leave questions and comments. I’ll update this post as I can; I’ll also do some step-by-step instructions for pieces of this puzzle.